Vulnerability management that everyone understands
Scan results that explain themselves.
The same scan data in two languages: a prioritised to-do list for your IT, and plain language with a traffic light for management.
Click at the top right: the same data, two views.
One platform, two languages
Everyone sees the same risk, in their own language.
Not two reports: SimpleSec shows the same findings twice, as a to-do list for IT and as plain language for management.
IT view
Prioritised fixes instead of 2,000 findings.
Reachability, asset importance and the exploit situation set the sequence. Each finding comes with step-by-step instructions and an effort estimate. No research needed.
3 critical · this week
Management view
Plain language and a traffic light instead of CVE numbers.
“Blackmail through encryption of your data is possible at the moment. Three measures break the chain. Effort: about two hours.” Every month, one page. Since December 2025, management must approve and supervise such measures personally (Section 38 BSIG). The monthly report is written for that duty.
Gets better every month
How it works
Three steps. No analyst needed.
Scan
External and internal, continuously. Appliance or cloud. Setup in one week.
Prioritise
2,000 findings become 3 that count this week, by reachability, asset importance and the exploit situation.
Understand
Instructions with the effort for IT. A monthly report in plain language with a traffic light for management.
Who is behind it
Why we build SimpleSec.
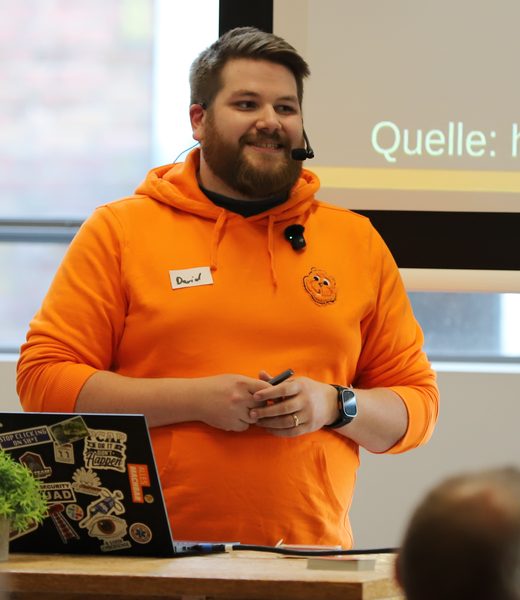
SimpleSec does not come from marketing, it comes from my daily work. For years I have tested company networks with the methods of attackers, as a security engineer. We see which three of 2,000 findings really count, and how to explain them so that people act. That is why we build SimpleSec.
David Fischer
FAQ
What you want to know first.
How long does the setup really take?
One week. Your IT places the appliance in your network and releases the scan ranges. After that, SimpleSec delivers the first prioritised report.
What does the appliance do in our network?
It scans the systems that you release, and it rates the findings. It changes nothing on your systems. You view the results in the cockpit.
Do we need our own analyst?
No. Your IT or your IT service provider works through the findings. Each finding comes with instructions and an effort estimate.
We already have an IT service provider.
Good. They fix the findings. SimpleSec shows you what is open and what it means. Both of you see the same state.
Does the report help with our cyber insurer?
The report documents which finding was fixed and when. Your insurer asks for this evidence in a claim.
Does NIS2 apply to us?
The German implementation act is in force since December 2025. It covers companies from 50 employees or 10 million euros of turnover in 18 sectors. The BSI self-check shows whether your company is in scope.
What does SimpleSec cost?
One price per company size band. It includes the appliance, the external scan and both reports. We name the number for your band in the first conversation.
For MSSPs and system integrators
Offer SimpleSec as a managed service.
One cockpit across all your customers. Each customer sees only itself.
Let's talk about your systems.
Setup in one week. Then you decide.
Request a demo